@Opcode_Networkon X · 2026-09-13
A tamper-evident, on-chain timestamp of what this post said. Captured 2026-09-13 19:11 UTC.
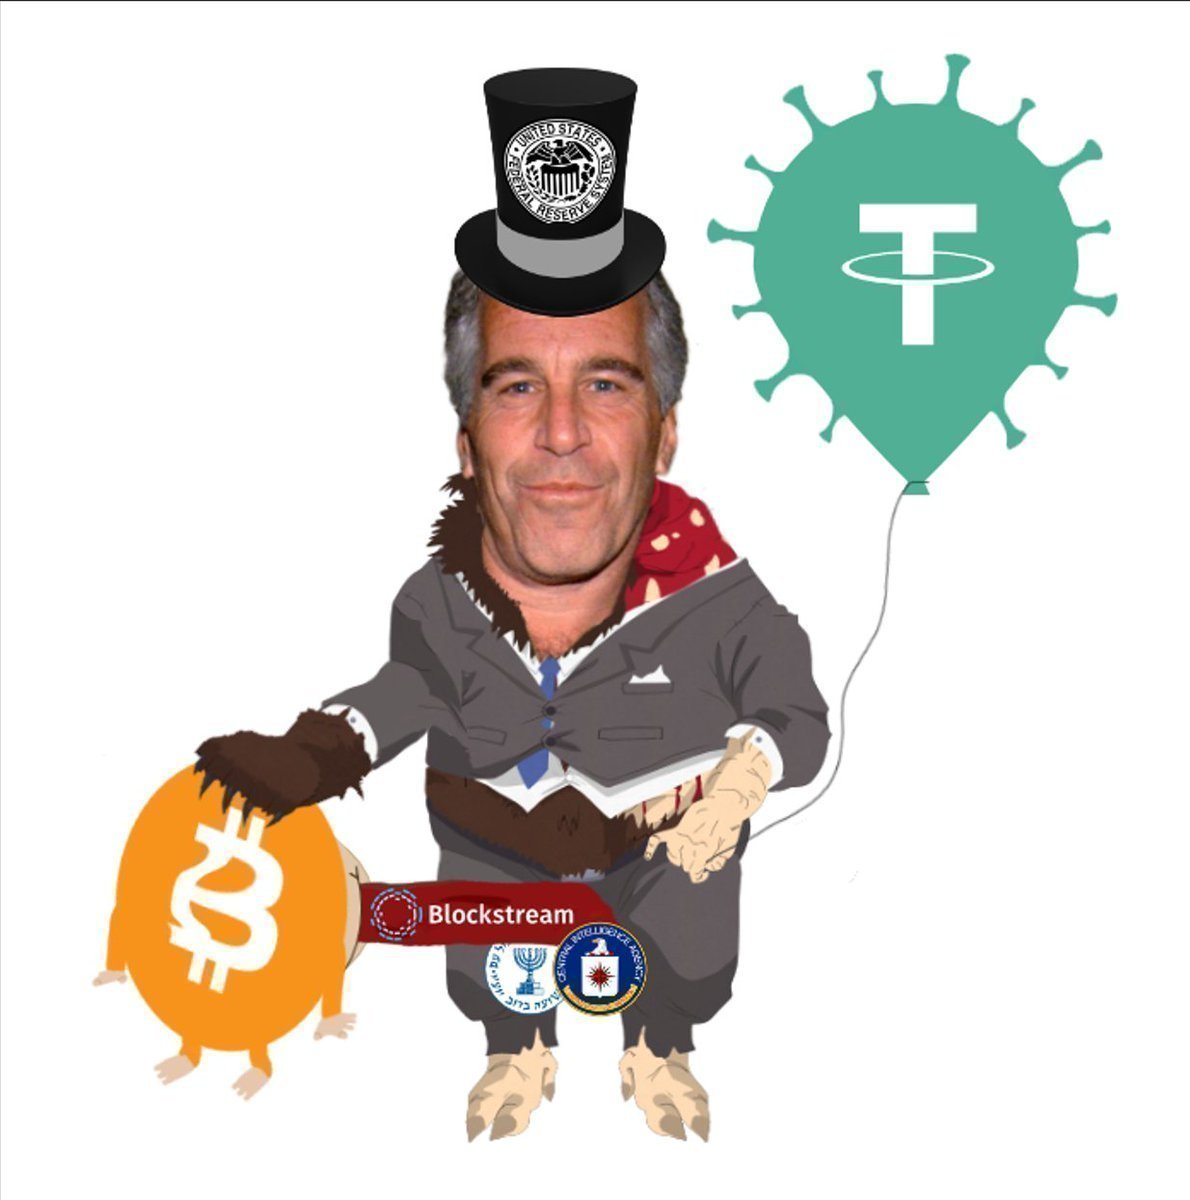
@twetchapp While that is true, the hijacked ultimately was finished through their proxy blockstream. Be careful tho, scammers like this ☝️ twetchapp account use it to steer people towards their scamcoin (BSV in this case). https://t.co/aCm3atQSsv
Verify it yourself: the manifest is the exact JSON whose
SHA-256 is e3554cfd60c424b169f78ba202d439baf7eeac558a3de45ddfe043d0adf504df; it binds the tweet id, author, post time, and the SHA-256 of the text above. Re-hash the text to match 6b64531d4a4e01f064794cac3bc2e5b4d1e72a8125955c665395f7ee57649158, and read the anchor transaction's OP_RETURN
bsv.cx / x1 / e3554cfd60c424b169f78ba202d439baf7eeac558a3de45ddfe043d0adf504df — the block's timestamp proves the post said this at or before that time,
with no trust in bsv.cx. Content archived via the X API.