@IntCyberDigeston X · 2026-09-12
A tamper-evident, on-chain timestamp of what this post said. Captured 2026-09-12 17:25 UTC.
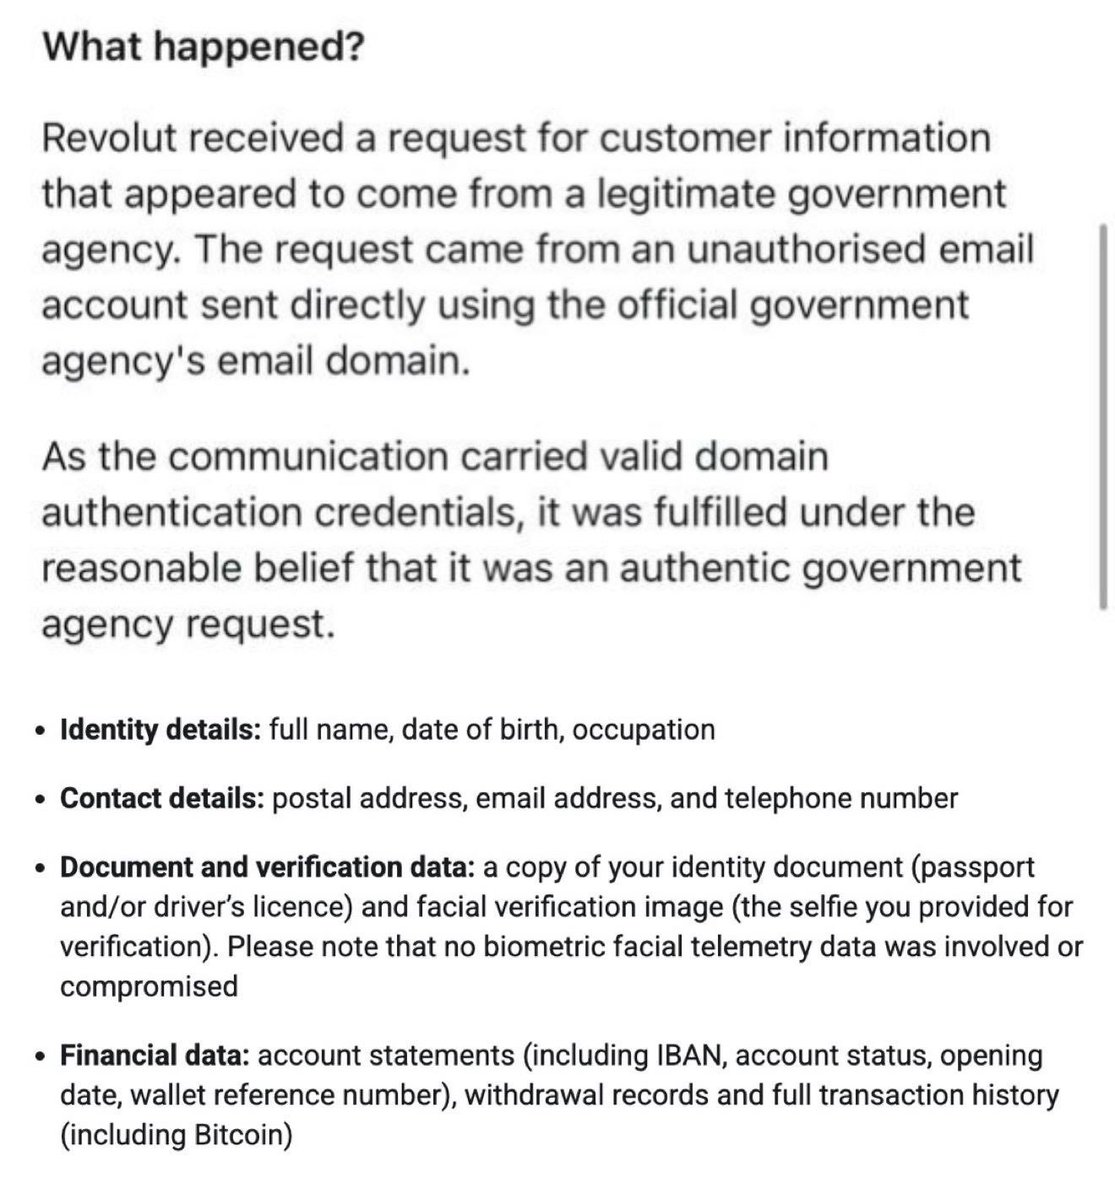
‼️ BREAKING: Revolut handed over customers’ passport copies, verification selfies and full transaction histories to a malicious actor. The actor sent lawful government information-demand emails using a genuine government domain that passed domain authentication. Revolut later concluded they were not authentic. Affected customers were notified on Friday. What may have been disclosed ranges from name, date of birth and home address to account statements, withdrawal records and complete Bitcoin transaction history. The company says it has alerted the agency to the unauthorised mailbox on its domain, blocked the address and begun notifying regulators. It has not named the agency, explained how someone obtained a mailbox there, or given a number of affected customers. ZachXBT, who circulated the notices, believes the incident was limited in size and aimed at high-net-worth users.
Verify it yourself: the manifest is the exact JSON whose
SHA-256 is bf21ae56e378bcf5421295da8bcf872c31c61b7bc079bbbc6d7413cf4c5dc8c6; it binds the tweet id, author, post time, and the SHA-256 of the text above. Re-hash the text to match 908e050530ab20db70f79e235743a00c42e2eefd669ea995c61e0b2acfcad5a4, and read the anchor transaction's OP_RETURN
bsv.cx / x1 / bf21ae56e378bcf5421295da8bcf872c31c61b7bc079bbbc6d7413cf4c5dc8c6 — the block's timestamp proves the post said this at or before that time,
with no trust in bsv.cx. Content archived via the X API.