@lengs4189on X · 2026-09-18
A tamper-evident, on-chain timestamp of what this post said. Captured 2026-09-19 20:33 UTC.
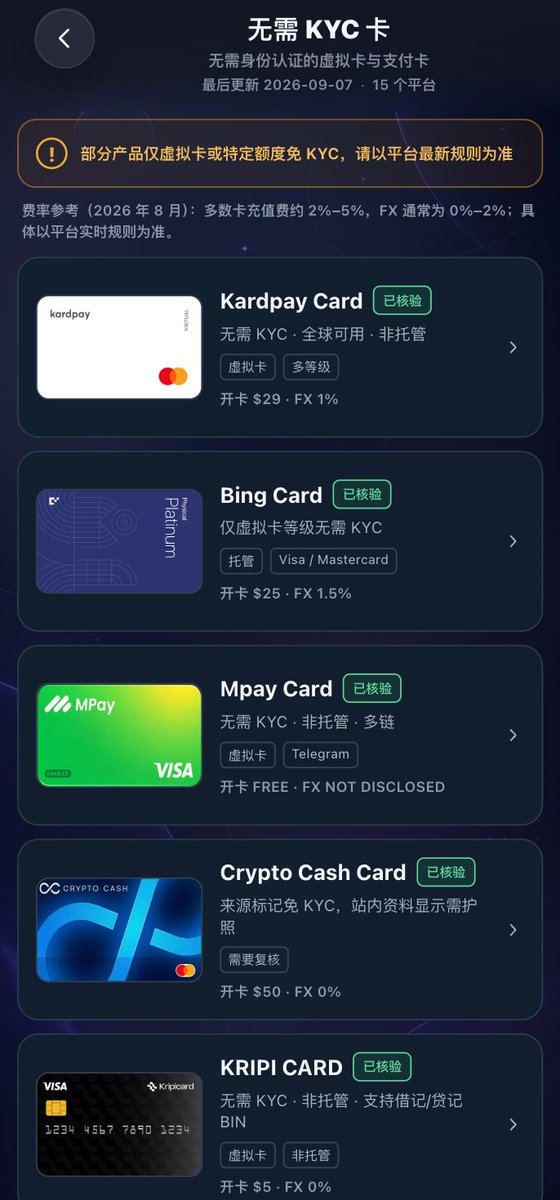
研究了一下,市面上很多“无需 KYC”的加密卡,大概率是这样来的: 卡商先用一家公司完成 KYB/KYC,开通企业卡账户,再把买卡的用户伪装成公司“员工”,批量创建员工虚拟卡。用户充值 USDT 后,卡商通过内部账户分配消费额度,并从开卡费、手续费和汇率差中赚钱。 最近有人注册了一张所谓的“No-KYC”加密卡,最后拿到的却是一张 Slash 卡。Slash 官方回应称,这并不是白标合作,而是有人滥用企业账户,把发放给公司的卡转卖给个人;平台发现后已经关闭了相关账户。 所以,这类卡并不是真的没有 KYC,只是 KYC 做在了卡商或其公司身上,最终用户看不到而已。 最大的问题是:卡不真正属于你,账户也不受你控制。一旦规模做大、交易异常或被上游发现,整批卡都可能被关闭,余额、退款和拒付也只能依赖卡商处理。 所谓“无需KYC卡”,很多时候只是别人的企业员工卡。能用不代表稳定,更不代表匿名,尽量随用随充,不要长期留余额。
Verify it yourself: the manifest is the exact JSON whose
SHA-256 is 09d101545ac9ad576484c7214f694aa3fb9c04a1738de320271e3d118197e853; it binds the tweet id, author, post time, and the SHA-256 of the text above. Re-hash the text to match 466f814d0e126881e7a7c95875b4d892dae61c3e58d783e951745468c624cfaa, and read the anchor transaction's OP_RETURN
bsv.cx / x1 / 09d101545ac9ad576484c7214f694aa3fb9c04a1738de320271e3d118197e853 — the block's timestamp proves the post said this at or before that time,
with no trust in bsv.cx. Content archived via the X API.